JADAPTIVE-SA-2026-001
Cross-User Public Key Authentication Bypass
- Advisory date
- 1 October 2026
- Status
- Fixed releases available
- CVE
- Not assigned
Summary
JADAPTIVE identified and corrected a vulnerability affecting public key authentication in Maverick SSH server products.
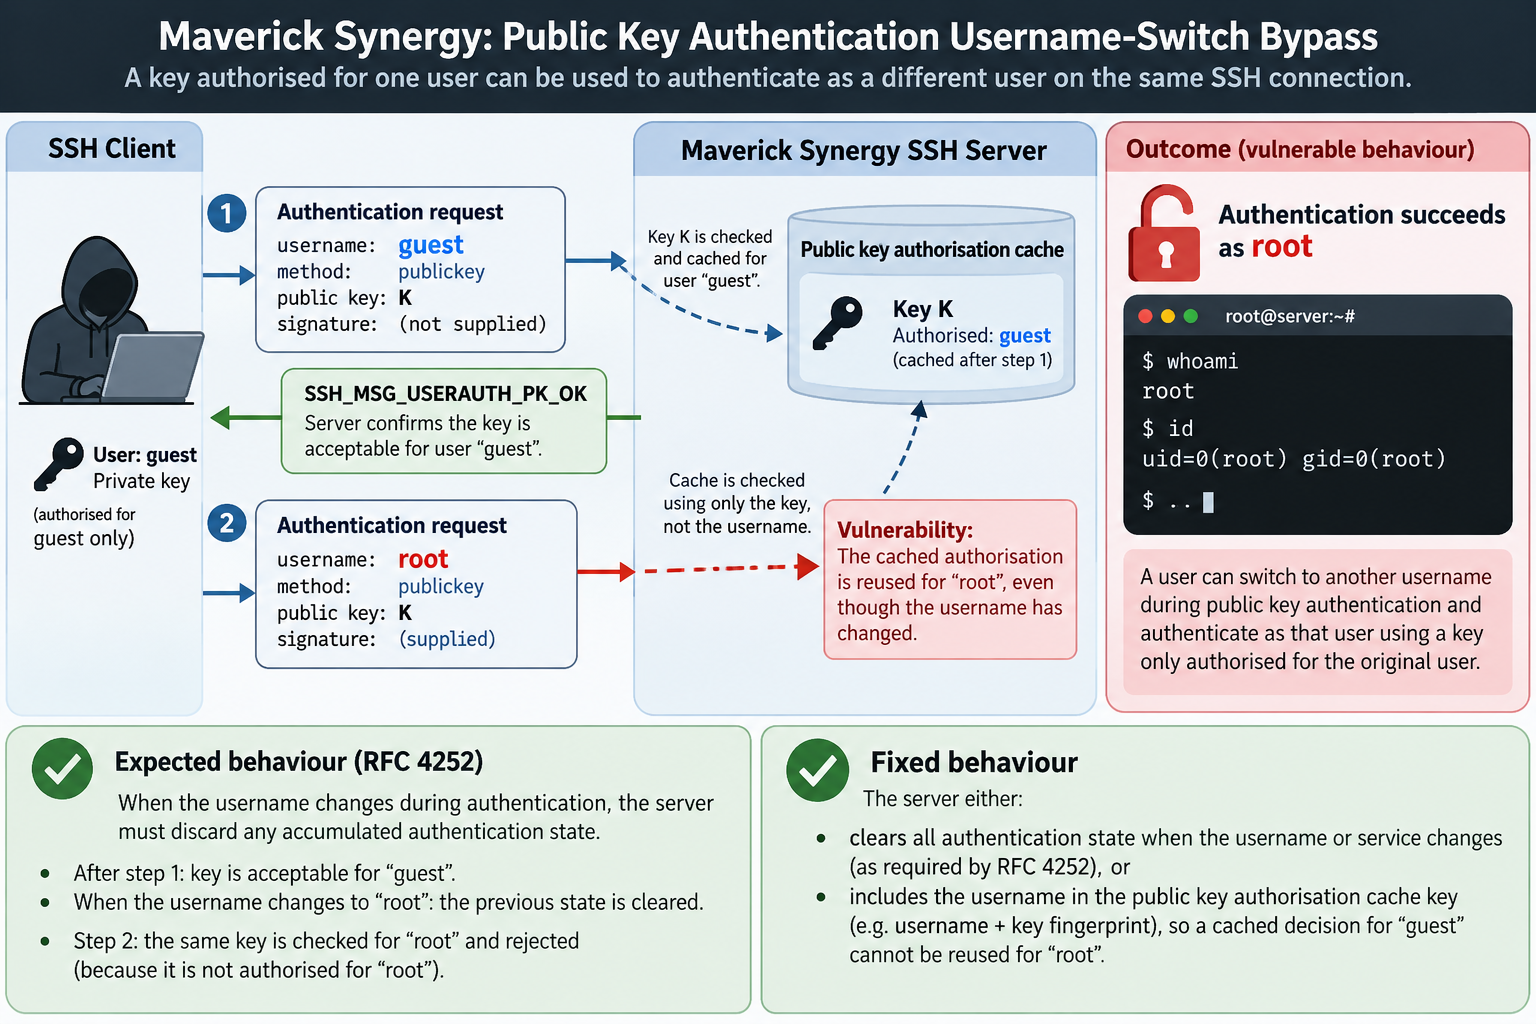
Under a specifically constructed authentication sequence, an accepted public key authorization decision could be reused after the username changed on the same SSH connection.
This could allow a client possessing a private key authorised for one account to authenticate as a different account without that key being authorised for the second account.
Affected Products
The vulnerability affects historical releases of:
- Maverick Synergy Server
- Maverick Synergy Server Hotfixes
- Maverick Legacy Server
The underlying behaviour is longstanding and is not limited to a single recent release.
Security Impact
An attacker who possesses a private key authorised for one account may be able to authenticate as another account by changing the requested username during the public key authentication sequence.
Successful exploitation requires public key authentication to be enabled, control of a private key authorised for at least one account, and a crafted sequence of authentication requests on the same connection.
The practical impact depends on the privileges and resources associated with the target account and the authorization model implemented by the application integrating Maverick.
Technical Description
The SSH authentication protocol includes the username in each `SSH_MSG_USERAUTH_REQUEST` message.
In affected versions, the connection username could change between authentication requests while a previously accepted public key fingerprint remained cached on the connection.
The cached authorization decision was associated with the public key fingerprint but was not bound to the username for which the original authorization check had been performed.
A subsequent signed public key request using the same key but a different username could therefore reuse the earlier authorization decision.
The signature still demonstrated possession of the private key. The vulnerability was a failure to preserve the association between the authenticated identity and its public key authorization decision.
- Relevant components
- `AuthenticationProtocolServer` and public key authorization caching.
- Relevant input
- Username in `SSH_MSG_USERAUTH_REQUEST`.
- Vulnerability class
- Improper authentication / cross-user authorization bypass.
Resolution
The correction enforces a consistent username and requested service throughout an SSH authentication sequence.
Once authentication has begun, a subsequent request that changes either the username or service causes the server to terminate the connection.
This prevents authentication state established for one identity from being reused for another identity on the same connection.
The behaviour is consistent with the requirements of RFC 4252 for handling changes to the username or service during authentication.
Regression tests confirm that the reported authentication sequence can no longer complete authentication as a second username.
Fixed Versions
| Product | Fixed version |
|---|---|
| Maverick Synergy Server | 3.2.0 |
| Maverick Synergy Hotfixes 3.1.x | 3.1.7 |
| Maverick Synergy Hotfixes 3.0.x | 3.0.33 |
| Maverick Legacy Server | 1.8.1 |
Recommended Action
Customers using affected Maverick server components should upgrade to the appropriate fixed release.
Deployments using public key authentication should be reviewed to assess potential exposure, particularly where different authenticated identities have access to different resources or permissions.
Customers unable to upgrade immediately should contact JADAPTIVE Support to discuss their circumstances and available remediation options.