JADAPTIVE-SA-2026-002
Mount Path Canonicalization Bypass in Virtual File System
- Advisory date
- 1 October 2026
- Status
- Fixed releases available
- CVE
- Not assigned
Summary
JADAPTIVE identified and corrected a vulnerability in virtual filesystem path canonicalization and mount selection affecting Maverick SSH server products.
Certain non-canonical path representations could cause the virtual filesystem to select a less restrictive parent mount instead of the intended child mount.
In affected configurations, this could allow operations to bypass access restrictions enforced by the child mount.
Affected Products
The vulnerability affects releases prior to the corrected versions of:
- Maverick Synergy Server
- Maverick Synergy Server Hotfixes
- Maverick Legacy Server
Exposure depends on the virtual filesystem mount configuration used by the integrating application.
Security Impact
A user may be able to access files or perform operations using the permissions of a parent mount instead of the more restrictive policy associated with a child mount.
Depending on the configuration, this could result in unauthorized read or write access to files that would otherwise be protected by the child mount.
The vulnerability requires a nested or overlapping mount configuration where the child mount's backing storage is accessible through the parent mount, and the child mount enforces a more restrictive policy.
Applications without such a configuration may not be exposed to this particular mount-selection bypass.
Technical Description
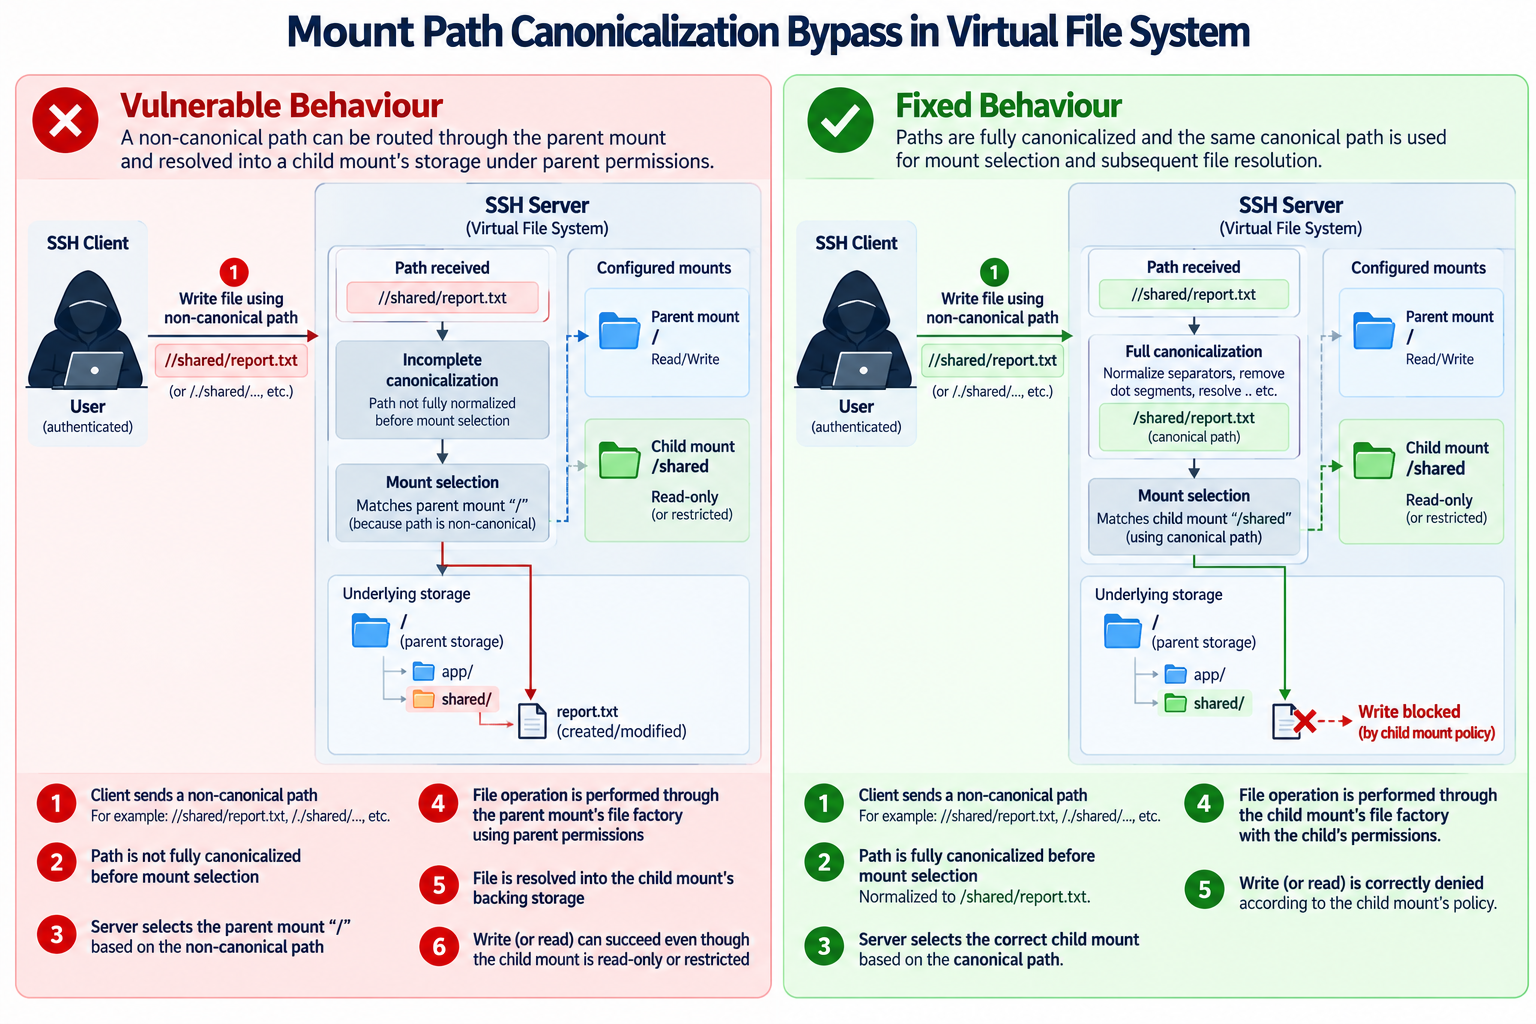
The vulnerability results from inconsistent canonicalization of virtual filesystem paths before mount selection.
In affected implementations, duplicate separators, dot segments, parent segments and certain separator representations were not consistently normalized before mount prefix matching.
Consequently, different representations of an equivalent path could be interpreted differently during mount selection and subsequent backing-store resolution.
A path intended for a restrictive child mount could instead be routed through the parent mount's file factory, allowing the operation to be evaluated using the parent's permissions.
- Relevant component
- `VirtualFileFactory.canonicalisePath` and virtual mount selection.
- Relevant input
- Virtual filesystem path supplied for file operations.
- Vulnerability class
- Path canonicalization / authorization bypass.
Example Configuration
Consider an application configured with the following virtual mounts:
| Virtual mount | Backing directory | Policy |
|---|---|---|
/ | /srv/sftp | Read/Write |
/shared | /srv/sftp/shared | Read-Only |
Under normal operation, requests targeting /shared should be handled by the child mount and subject to its read-only policy.
In affected implementations, a non-canonical representation of a path under /shared could fail to select the child mount and instead be processed through the parent mount.
Because the child directory is also reachable through the parent mount's backing storage, this could allow an operation that the child mount would otherwise deny.
This example illustrates the required configuration. The vulnerability does not imply that all Maverick virtual filesystem deployments are affected.
Resolution
The correction ensures that virtual paths are consistently canonicalized before the security-sensitive mount-selection decision.
The remediation includes:
- Normalizing path separators consistently.
- Collapsing duplicate separators.
- Removing dot segments.
- Resolving parent segments consistently.
- Applying canonical absolute paths during mount matching.
- Adding regression tests covering equivalent path representations.
Mount selection and backing-store resolution now operate on a consistent canonical representation of the requested virtual path.
Regression testing confirms that non-canonical representations cannot bypass the intended child mount's policy in the affected test configurations.
Fixed Versions
| Product | Fixed version |
|---|---|
| Maverick Synergy Server | 3.2.0 |
| Maverick Synergy Hotfixes 3.1.x | 3.1.7 |
| Maverick Synergy Hotfixes 3.0.x | 3.0.33 |
| Maverick Legacy Server | 1.8.1 |
Recommended Action
Customers should upgrade to the appropriate fixed release.
Applications using nested or overlapping virtual filesystem mounts should review whether more restrictive child mounts are backed by storage reachable through less restrictive parent mounts.
Customers who require assistance evaluating their configuration or upgrading should contact JADAPTIVE Support.